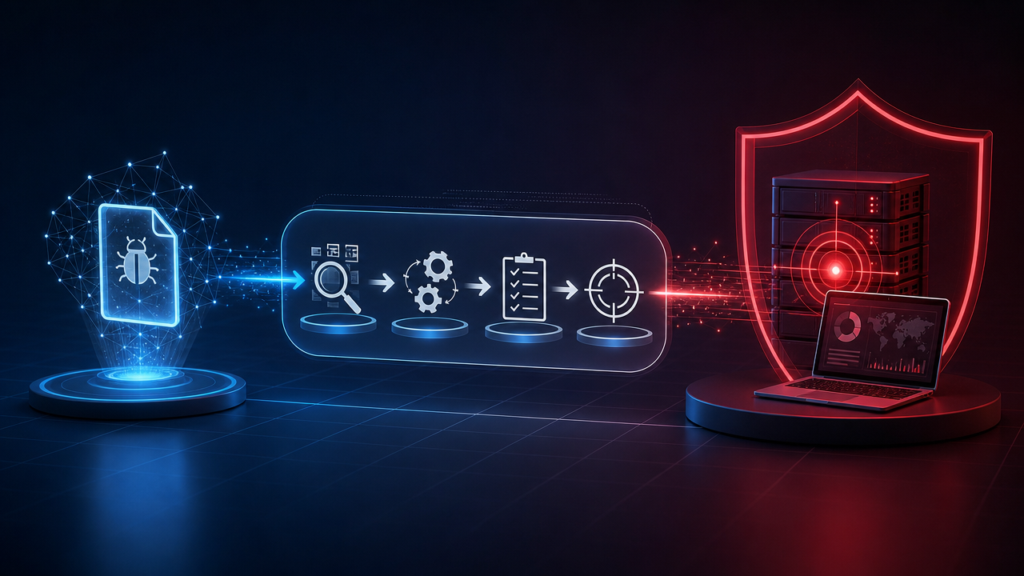
A vulnerability scanner tells you a CVE matches your installed version. It does not tell you whether that CVE is actually reachable, actually exploitable, in your specific configuration — a locked-down environment can carry a “critical” finding that’s functionally inert, while a seemingly minor one, chained with something else, is a live path to compromise. Automated Exposure Validation (AEV) is the CTEM stage built to close that exact gap: it takes a theoretical finding and safely confirms whether it’s genuinely exploitable before anyone spends remediation effort on it.
Malware detection is a useful lens into why this distinction matters in practice. A file that matches a malware signature is a validated finding — it’s there, it’s active, it needs immediate response. A CVE that matches a plugin version, with no confirmation the vulnerable code path is even reachable, is still theoretical. Treating both the same way — as equally urgent “vulnerabilities” — is precisely the prioritization error AEV exists to prevent.
Contents
1. Introduction & Context
Most vulnerability management tooling stops at version matching: it identifies which CVEs correspond to the software versions running in an environment and reports all of them as findings. That list is a starting point, not an answer — it says nothing about whether the vulnerable code path is actually reachable from outside the network, whether a prerequisite condition for exploitation is even present, or whether an existing control already blocks the attack in practice. Treating every version match as equally urgent produces exactly the alert fatigue that causes real, exploitable findings to get lost among theoretical ones.
Automated Exposure Validation is the discipline of closing that gap continuously rather than through occasional manual review. This guide covers why a CVE match and a confirmed risk are different things, uses malware detection as a contrasting example of a finding that’s validated by definition, and walks through building a triage process that separates the two categories before remediation effort gets allocated.
2. Business Impact
The scale of the theoretical-versus-validated gap is larger than most security teams assume. Research from Kenna Security (now part of Cisco) and the Cyentia Institute, published in the Prioritization to Prediction series, found that only an estimated 2–5% of publicly disclosed vulnerabilities are ever actually observed being exploited in the wild — meaning the overwhelming majority of a typical scan’s findings are, by definition, theoretical. IBM’s Cost of a Data Breach Report 2026 places the average breach cost at $4.99M USD — the highest figure on record — a cost that falls disproportionately on the small fraction of findings that were both real and missed.
| Validation Gap | Business Consequence | Regulatory Exposure | Severity |
| All CVE matches treated as equally urgent | Remediation effort spent on non-exploitable findings while real risk waits | SOC 2 CC7.1 | MEDIUM |
| No confirmation the vulnerable code path is reachable | False sense of urgency drives alert fatigue; real findings get lost in noise | NIST CSF ID.RA-5 | HIGH |
| No distinction between “present” and “active” compromise (e.g. malware) | Delayed response to a genuinely active incident | PCI DSS Req. 11.5 | CRITICAL |
| No re-validation after environment changes | A previously non-exploitable finding becomes exploitable after an unreviewed config change | ISO 27001 A.12.6 | HIGH |
| Compliance evidence based on raw scan output, not validated findings | Weaker audit posture — auditors distinguish scan output from confirmed risk | PCI DSS Req. 11.3 | MEDIUM |
The operational payoff of closing this gap isn’t abstract: every hour a team spends confirming and remediating a finding that was never actually exploitable is an hour not spent on the small percentage of findings that genuinely matter. Validation doesn’t reduce the total number of CVEs disclosed against an environment — it redirects finite remediation capacity toward the ones that are real.
3. Anatomy of the Gap: Theoretical vs. Validated Exposure
3.1 Why a CVE Match Isn’t the Same as Confirmed Risk
A version-matching scanner answers one question: does this software version have a known CVE. It cannot answer several others that determine whether that CVE poses real risk in a specific environment — is the vulnerable function actually reachable given the site’s configuration, does exploitation require a precondition (a specific setting enabled, a particular user role) that isn’t present, and is there already a compensating control, like a WAF rule, that blocks the exploitation pattern in practice. A finding that fails any of these checks is not exploitable today, regardless of what its CVSS score implies.
3.2 Malware Detection: The Validated-by-Definition Case
Malware and backdoor detection sit at the opposite end of the spectrum from a raw CVE match, and the contrast is instructive:
| THE VALIDATION SPECTRUM: THEORETICAL (unvalidated CVE match) — Installed version matches a known CVE — Reachability and preconditions unconfirmed — Requires validation before prioritization is meaningful VALIDATED (confirmed exploitable) — Vulnerable code path confirmed reachable — Exploitation preconditions confirmed present — Requires immediate remediation or a compensating control CONFIRMED ACTIVE (e.g. malware / backdoor signature match) — Malicious code is present and executable on the system now — Nothing left to validate — compromise is not hypothetical — Requires immediate incident response, not standard triage |
Routing a malware finding into the same queue as an unvalidated CVE match — to be triaged in order of CVSS score alongside everything else — introduces exactly the kind of delay an active compromise cannot afford. The two categories require fundamentally different response speeds, and a triage process that doesn’t distinguish them will systematically under-respond to the more urgent one.
3.3 WordPress as the Recurring Case Study
WordPress plugin vulnerability reports illustrate the reachability problem clearly. A plugin CVE is frequently scoped to a specific, non-default configuration — a particular setting enabled, an integration most installations don’t use, or a function only reachable by an authenticated admin session that an external scanner never obtains. A vulnerability scanner that only checks the installed version has no way to know whether that precondition applies to a specific site. Two installations running the identical vulnerable plugin version can have entirely different real-world risk, and only validation — not the version number alone — reveals which one.
4. Proactive Detection with the Teisoft Exposure Platform
The Teisoft Exposure Platform treats validation as a first-class stage of its detection cycle, not an optional add-on to raw CVE scanning. Every finding surfaced through continuous External Asset Discovery is run through Automated Exposure Validation (AEV) — safe, non-destructive confirmation of reachability and exploitability — before it’s assigned a priority, so a critical-looking finding that isn’t actually reachable doesn’t compete for attention with one that is.
4.1 What Automated Validation Adds
- Reachability confirmation: Verifies whether a vulnerable code path is actually accessible from outside the network before treating a version match as urgent.
- Safe exploit-path testing: Uses non-destructive techniques to confirm exploitability without executing a payload that could disrupt production systems.
- Integrated malware and integrity signals: Confirmed malware or backdoor detections are flagged as immediately actionable, distinct from the standard CVE triage queue.
- Confidence-scored findings: Every finding is labeled by validation state — theoretical, validated, or confirmed active — rather than a single undifferentiated severity score.
- Continuous re-validation: Findings previously dismissed as non-exploitable are re-checked as the environment changes, rather than validated once and forgotten.
| Validation Task | Manual Process | Teisoft Automated |
| Confirm code path reachability | Manual review of configuration and access controls | Automated, per finding |
| Safe exploitability confirmation | Requires a skilled tester, scheduled periodically | Continuous, non-destructive |
| Distinguish malware from theoretical CVE | Manual triage, inconsistent prioritization | Automatic categorization |
| Re-validate after environment change | Rarely done — depends on someone remembering | Continuous |
The platform delivers a prioritized findings report that leads with confirmed and active findings, followed by validated exploitable risk, with unvalidated theoretical matches tracked separately rather than mixed into the same urgent queue.
| → Run your free External Attack Surface Scan |
| teisoftllc.com/free-vulnerability-scan/ — find out in minutes which findings on your external assets are validated, exploitable risk, not just a theoretical CVE match. |
5. Step-by-Step: Building a Validation-First Triage Process
The following five-step process separates confirmed risk from theoretical findings before remediation effort is allocated.
Step 1: Separate “Detected” from “Validated” in Your Tracking
Add a validation-state field to however findings are tracked today — even a simple spreadsheet column separating “version match only” from “confirmed exploitable” is a meaningful improvement over a single undifferentiated list.
Step 2: Confirm Reachability Before Assigning Priority
Before treating a CVE match as urgent, check whether its documented preconditions apply: is the affected function reachable without authentication, is the vulnerable setting or integration actually enabled, and is the endpoint reachable from outside the network at all.
Step 3: Run Safe, Non-Destructive Exploit Confirmation
Where reachability is confirmed, validate exploitability using non-destructive methods only — confirming a code path executes as expected without delivering an actual payload against production. This is a specialized skill; where in-house capability doesn’t exist, an automated validation platform or a controlled penetration test fills the gap without risking production stability.
Step 4: Integrate Malware Signals as Confirmed-by-Default
Configure malware and file-integrity detections to bypass the standard CVE triage queue entirely and route directly to incident response. There is no reachability or exploitability question to answer — the finding is already confirmed active by its nature.
Step 5: Re-Validate on Environment Change
Any configuration change, new integration, or plugin update should trigger re-validation of previously dismissed findings — a code path that was unreachable last month can become reachable after a single settings change nobody thought to review against the open findings list.
Validation Triage: Before / After
| Element | State Before | State After | Improvement |
| Finding classification | Single undifferentiated severity list | Theoretical / validated / confirmed active, tracked separately | Prioritization accuracy improved |
| Malware response time | Queued alongside theoretical CVEs | Routed directly to incident response | Response delay eliminated |
| Reachability confirmation | Not performed — CVSS score alone drives priority | Confirmed before priority assignment | False urgency reduced |
| Re-validation cadence | None — validated once, if ever, and forgotten | Triggered by environment change | Drift-related risk caught early |
6. Frequently Asked Questions (FAQ)
Q: If a CVE isn’t validated as exploitable, does that mean it’s safe to ignore?
No — it means it’s lower priority than a validated finding, not risk-free. An unreachable code path today can become reachable after a configuration change, a new integration, or a permissions update. Unvalidated findings should stay tracked and be re-checked on a schedule; they should not be treated as equally urgent as a confirmed one.
Q: How does automated validation differ from a manual penetration test?
Automated validation runs continuously and confirms exploitability at scale using safe, non-destructive techniques — it answers ‘is this specific finding reachable and exploitable right now.’ A penetration test is periodic, human-led, and goes further: it chains multiple findings together to demonstrate a complete attack path, including business-logic flaws no automated tool can identify. The two are complementary, not substitutes for each other.
Q: Can automated exposure validation techniques accidentally cause harm or downtime?
A properly designed validation process uses safe, non-destructive confirmation methods specifically to avoid this — verifying that a vulnerable code path is reachable and that preconditions for exploitation are met, without executing an actual payload against production systems. This is a deliberate design constraint, not an incidental safety measure.
Q: Why treat malware detection differently from CVE-based vulnerability findings?
A malware or backdoor signature match is not a theoretical risk — the malicious code is already present and active. There’s nothing to validate about reachability or exploitability; the finding is confirmed by definition. Routing it into the same triage queue as an unvalidated CVE match introduces delay into what should be an immediate response.
Q: Does validated-exposure data hold up better under a compliance audit than raw scan output?
Generally, yes. A QSA or auditor reviewing evidence based only on a vulnerability scan’s raw output is looking at a list of theoretical findings with no confirmation of real-world risk. Evidence that includes validation — confirming which findings are genuinely exploitable — demonstrates a more mature process and is typically viewed more favorably during PCI DSS and SOC 2 review.
7. Conclusion & Next Steps
- A CVE matching an installed software version is a theoretical finding, not a confirmed risk — research from Kenna Security and the Cyentia Institute suggests only 2–5% of disclosed vulnerabilities are ever actually exploited in the wild. Treating every match as equally urgent guarantees that remediation effort is misallocated most of the time.
- Malware and backdoor detection sit at the opposite end of the spectrum: there is nothing to validate, because the compromise is already active. A triage process that doesn’t route confirmed-active findings to immediate response separately from theoretical CVE matches will systematically under-respond to the more urgent category.
- The five-step process in this guide — separating detected from validated, confirming reachability, safely testing exploitability, fast-tracking confirmed-active findings, and re-validating on environment change — redirects finite remediation capacity toward the small fraction of findings that are genuinely exploitable.
| → Primary CTA: External Attack Surface Scan (Free) |
| Run your free External Attack Surface Scan at teisoftllc.com/free-vulnerability-scan/ and find out in minutes which findings on your external assets are validated, exploitable risk — not just a theoretical CVE match. |
| → Secondary CTA: Continuous Penetration Testing |
| Automated validation confirms a single finding is reachable and exploitable. Penetration testing goes further, chaining multiple validated findings into a complete attack path using human adversarial judgment no automated tool replicates. Teisoft’s Continuous Penetration Testing service provides that deeper layer of confirmation on an ongoing basis. Contact Teisoft |
Related Resources on teisoftllc.com
Validation is the fourth of five stages in Teisoft’s CTEM cycle — see our guide to CTEM’s five stages for how it connects to discovery, prioritization, and remediation governance.
- CTEM Explained: The 5 Stages of Continuous Threat Exposure Management
- How to Read CVE Alerts: CVSS, Scope, and Priority
- Vulnerable Third-Party Components: Detection and Management at Scale