Ask a security team how they prioritize vulnerabilities and most will say “by CVSS score” — and most of them are quietly misallocating remediation effort as a result. CVSS measures theoretical severity: how bad a vulnerability could be if exploited. It says nothing about whether anyone is actually exploiting it. A CVSS 9.8 finding with no working exploit in the wild is, in practical terms, less urgent than a CVSS 6.5 already being used in active attacks — and CVSS alone cannot tell the two apart.
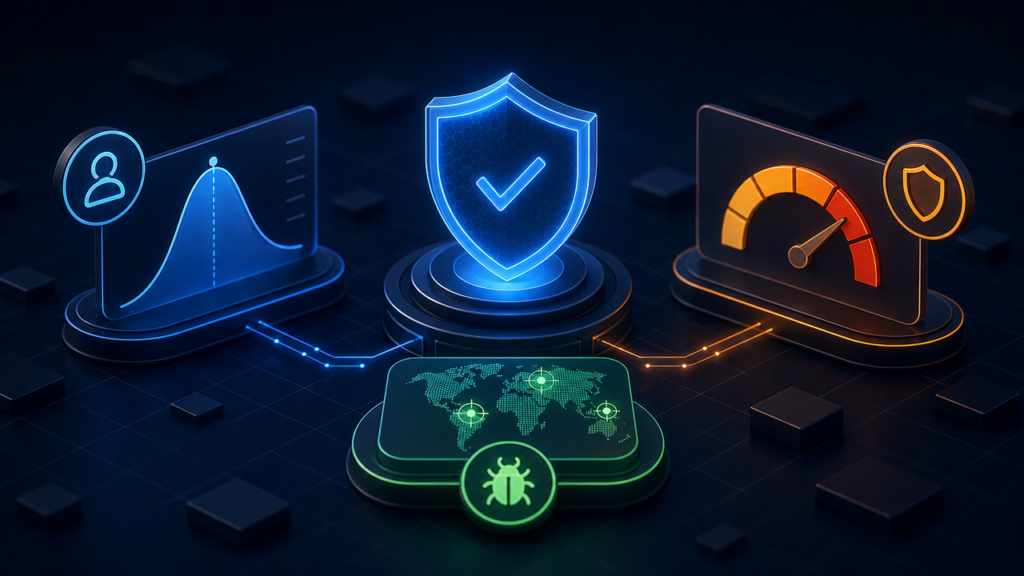
Risk-based vulnerability prioritization closes that gap by combining three independent signals — CVSS for potential severity, EPSS for the probability of real-world exploitation, and the CISA KEV catalog for confirmed active exploitation — into a single decision framework. None of the three is sufficient alone; together, they separate the vulnerabilities worth an emergency response from the much longer list that isn’t.
Contents
1. Introduction & Context
Every vulnerability management program eventually confronts the same operational problem: more CVEs get published every week than any team can remediate in the same period, and a scoring system that treats all of them as roughly equally urgent guarantees that real, actively exploited risk gets lost in a queue of theoretical findings. CVSS, published for nearly every CVE, was never designed to solve this — it measures severity in isolation from real-world context, which is precisely why using it as the sole prioritization input produces systematic errors in both directions: over-response to findings that pose no practical threat, and under-response to lower-scored findings that are already being exploited at scale.
This guide compares the three data sources that, combined, solve the prioritization problem CVSS alone cannot: CVSS itself, the Exploit Prediction Scoring System (EPSS), and the CISA Known Exploited Vulnerabilities (KEV) catalog. It covers what each one actually measures, where each one is insufficient on its own, and a concrete matrix and workflow for combining all three into a single prioritization decision.
2. Business Impact
The cost of CVSS-only prioritization is not evenly distributed — it concentrates in the small number of cases where the scoring gets it wrong at the worst possible moment. IBM’s Cost of a Data Breach Report 2026 places the average breach cost at $4.99M USD — the highest figure on record — and research from Kenna Security and the Cyentia Institute has found that only an estimated 2–5% of published vulnerabilities are ever observed being exploited in the wild, meaning a CVSS-only approach spends the overwhelming majority of its remediation effort on findings that were never actually going to be used against the organization.
| Prioritization Error | Operational Consequence | Regulatory Exposure | Severity |
| High-CVSS, near-zero EPSS finding treated as emergency | Emergency change process consumed, change-fatigue for future findings | SOC 2 CC7.1 | MEDIUM |
| Moderate-CVSS finding with high EPSS deprioritized | Actively-trending exploitation missed while lower-priority items get attention first | PCI DSS Req. 6.3.3 | HIGH |
| KEV-listed finding not flagged as an override | Confirmed active exploitation treated as routine rather than urgent | CISA BOD 22-01 (federal); best practice elsewhere | CRITICAL |
| No re-scoring cadence for EPSS drift | A finding’s exploitation probability rises sharply post-triage and nobody notices | NIST CSF ID.RA-5 | HIGH |
The strategic payoff of combining all three scores isn’t a reduction in the number of CVEs disclosed against an environment — it’s a redirection of a security team’s genuinely limited remediation capacity toward the small fraction of findings that carry real, confirmed risk, instead of spreading that capacity evenly across a list where severity score and actual danger are only loosely correlated.
3. Anatomy of Prioritization: CVSS, EPSS, and KEV Compared
3.1 Why CVSS Alone Is Not Enough: The False Urgency Problem
CVSS scores what a vulnerability could do in the worst case, assuming it is exploited — not whether anyone is exploiting it, and not how likely that is to change. Two findings with identical CVSS 9.8 scores can have wildly different real-world urgency: one might require a rare, specific configuration to exploit and have no known working attack, while the other has a public proof-of-concept and is already being scanned for at scale. CVSS treats both identically. That gap between theoretical maximum severity and actual observed risk is the false urgency problem, and it is the core reason CVSS was never intended to be used alone for prioritization — a point CVSS’s own maintainers at FIRST.org have stated explicitly.
3.2 CVSS: What It Actually Measures
The Common Vulnerability Scoring System produces a 0–10 severity score from a vector string describing exploitation preconditions (attack vector, complexity, privileges required, user interaction) and impact (confidentiality, integrity, availability). It is a standardized, comparable severity measure — useful for understanding what happens if a vulnerability is exploited, and largely silent on the separate question of whether it will be.
3.3 EPSS: Probability of Exploitation
The Exploit Prediction Scoring System, maintained by FIRST.org, estimates the probability that a given CVE will be exploited in the wild within the next 30 days, expressed as a percentage. Where CVSS is static once published, EPSS is dynamic — it’s recalculated daily as new signals (public proof-of-concept code, scanning activity, chatter in exploit communities) become available, meaning the same CVE’s score can move dramatically within days of publication.
How EPSS Scores Are Calculated
EPSS is a machine learning model trained on historical data about which CVEs were actually exploited, correlated against dozens of features per vulnerability — the software vendor, the vulnerability type, references to public exploit code, and observed scanning traffic tied to the CVE. The output is not a guess; it’s a probability calibrated against a large historical dataset of confirmed exploitation events, which is why it tends to reflect real-world attacker behavior more closely than severity scoring alone.
3.4 CISA KEV: Confirmed Active Exploitation
The Known Exploited Vulnerabilities catalog, maintained by the U.S. Cybersecurity and Infrastructure Security Agency, is neither a severity score nor a probability — it’s a confirmed fact: every CVE on the list has documented evidence of active exploitation in the wild. Where EPSS estimates likelihood, KEV states certainty for the subset of vulnerabilities it covers. CISA’s Binding Operational Directive 22-01 mandates remediation of KEV-listed vulnerabilities within 14 days for U.S. federal agencies — a deadline enterprise programs generally treat as a reasonable external benchmark even where the directive itself doesn’t apply.
3.5 Combining the Three: A Prioritization Matrix
Each score answers a different question — CVSS asks how bad, EPSS asks how likely, KEV states whether it’s already happening. Combined, they produce a far more reliable priority signal than any one alone:
| CVSS | EPSS | KEV Listed? | Priority | Typical SLA |
| Any | Any | Yes | P1 — Emergency | < 24 hours (14 days under BOD 22-01) |
| 9.0+ | > 0.70 | No | P1 — Emergency | < 4 hours |
| 7.0–8.9 | > 0.50 | No | P2 — Priority | < 24 hours |
| 9.0+ | < 0.10 | No | P3 — Standard | < 14 days |
| 4.0–6.9 | > 0.50 | No | P2 — Priority | < 24–72 hours |
| 4.0–6.9 | < 0.10 | No | P4 — Routine | < 30 days |
| < 4.0 | Any | No | P4 — Routine | < 30 days |
The practical rule embedded in this matrix: KEV listing always overrides both other scores, and an EPSS score above roughly 0.50 should elevate priority at least one tier above what CVSS alone would suggest — a CVSS 7.5 with EPSS 0.90 is operationally more urgent than a CVSS 9.8 with EPSS 0.01.
4. Proactive Detection with the Teisoft Exposure Platform
The Teisoft Exposure Platform applies exactly this combined scoring model as part of its Risk-Based Vulnerability Management capability, rather than surfacing raw CVSS scores and leaving the CVSS-versus-EPSS-versus-KEV reconciliation to the security team manually. Every finding discovered through continuous External Asset Discovery is scored against all three sources before it’s presented, and confirmed exploitable through Automated Exposure Validation (AEV) — so the finding a team sees at the top of their queue is both theoretically severe and practically urgent, not merely one or the other.
4.1 What the Platform Adds to Manual Triage
- Automatic KEV cross-reference: Every finding is checked against the current CISA KEV catalog and flagged as an override the moment it’s listed, without waiting for a manual review cycle.
- Continuous EPSS re-scoring: Findings are re-evaluated as EPSS scores change daily, surfacing priority shifts instead of relying on the score captured at initial triage.
- Combined matrix scoring: Findings are pre-sorted using the CVSS + EPSS + KEV matrix rather than requiring each analyst to reconcile three separate data sources by hand.
- Exploitability confirmation via AEV: Where feasible, findings are further validated for actual reachability and exploitability in the specific environment, adding a fourth signal beyond the three industry-standard scores.
| → Run your free External Attack Surface Scan |
| teisoftllc.com/free-vulnerability-scan/ — find out in minutes which findings on your external assets are genuinely high priority once CVSS, EPSS, and KEV are considered together. |
5. Step-by-Step: Operationalizing a Combined Prioritization Matrix
The following steps turn the matrix in Section 3 into a working part of a team’s vulnerability management process.
Step 1: Pull All Three Scores for Every Finding
| # ── Pull CVSS score from NVD for a given CVE ─────────────────────── curl -s “https://services.nvd.nist.gov/rest/json/cves/2.0?cveId=CVE-YYYY-NNNNN” | \ python3 -c “import sys,json; d=json.load(sys.stdin); print(d[‘vulnerabilities’][0][‘cve’][‘metrics’][‘cvssMetricV31’][0][‘cvssData’][‘baseScore’])” # ── Pull EPSS score from FIRST.org’s public API ──────────────────── curl -s “https://api.first.org/data/v1/epss?cve=CVE-YYYY-NNNNN” | \ python3 -c “import sys,json; print(json.load(sys.stdin)[‘data’][0][‘epss’])” # ── Check CISA KEV catalog membership ────────────────────────────── curl -s “https://www.cisa.gov/sites/default/files/feeds/known_exploited_vulnerabilities.json” | \ python3 -c “import sys,json; kev=json.load(sys.stdin); ids={v[‘cveID’] for v in kev[‘vulnerabilities’]}; print(‘CVE-YYYY-NNNNN’ in ids)” |
Step 2: Apply the Matrix to Assign Priority
Run each finding’s three scores against the matrix in Section 3.5. KEV membership is checked first and overrides everything else; where it’s absent, CVSS and EPSS are evaluated together.
Step 3: Set an Explicit SLA per Priority Tier
A priority tier without a committed response time is a suggestion, not a policy. Document the SLA for each tier from the matrix and make it the standard your team is measured against — P1 within 4 hours, P2 within 24 hours, and so on.
Step 4: Re-Score on a Recurring Cadence
EPSS scores shift daily and KEV listings are added continuously. A finding scored once at triage and never revisited will miss exactly the kind of priority escalation this framework exists to catch — schedule automated re-scoring rather than treating the initial score as permanent.
Step 5: Document the Decision for Audit Evidence
Record which scores drove each priority assignment and when. A QSA or auditor reviewing a vulnerability management process responds far better to “here is the CVSS, EPSS, and KEV status that produced this priority” than to an unexplained severity label with no documented rationale.
Prioritization Workflow: Before / After
| Element | State Before | State After | Improvement |
| Scoring inputs | CVSS only | CVSS + EPSS + KEV combined matrix | False urgency reduced |
| KEV-listed findings | Scored the same as any other finding | Automatic override to P1 | Active exploitation never missed |
| Re-evaluation | Scored once at triage, never revisited | Recurring automated re-score | Drift caught early |
| Audit evidence | Unexplained severity label | Documented scores behind each decision | QSA-ready rationale |
6. Frequently Asked Questions (FAQ)
Q: If EPSS already predicts exploitation probability, why do we still need CVSS at all?
EPSS predicts likelihood, not impact. A vulnerability with a high EPSS score but low CVSS impact metrics (say, a minor information disclosure) may still be lower priority than a lower-EPSS finding that would grant full system compromise if exploited. The two scores answer different questions — how likely, and how bad — and prioritization requires both.
Q: Does a CVE listed in the CISA KEV catalog automatically outrank everything else?
In practice, yes, for organizations subject to CISA’s Binding Operational Directive 22-01, and it’s a reasonable default for any organization: KEV listing means confirmed active exploitation is already occurring, which is a stronger signal than either CVSS or EPSS alone provide. Treat KEV membership as an override that elevates priority regardless of what the other two scores say.
Q: How often do EPSS scores change, and do we need to re-check them constantly?
EPSS scores are recalculated daily by FIRST.org as new exploitation data becomes available, and can shift significantly — a score of 2% can become 80% within days of a working exploit becoming public. Findings previously deprioritized on EPSS grounds should be re-evaluated on a recurring basis, not scored once and left alone.
Q: Our team already uses CVSS-only triage — what’s the actual cost of not adding EPSS and KEV?
CVSS-only triage systematically misprioritizes in both directions: high-CVSS findings with near-zero real-world exploitation consume emergency response capacity, while lower-CVSS findings already being actively exploited wait in a standard patch cycle. The cost isn’t a single incident — it’s a persistent misallocation of a security team’s most limited resource, its attention.
Q: Can this prioritization matrix be automated, or does it require manual review of every finding?
The scoring inputs — CVSS from the CVE record, EPSS from FIRST.org’s API, and KEV status from CISA’s published catalog — are all machine-readable and can be pulled and combined automatically. Manual review is still valuable for edge cases the matrix doesn’t cleanly resolve, but the bulk of triage can run without a human checking each individual score.
7. Conclusion & Next Steps
- CVSS measures theoretical severity, not real-world urgency — using it alone produces the false urgency problem, where findings get equal weight regardless of whether anyone is actually exploiting them. EPSS adds a dynamic probability of exploitation; the CISA KEV catalog adds confirmed certainty for the subset already being actively used.
- The combined matrix in this guide treats KEV listing as an automatic override and elevates priority when EPSS exceeds roughly 0.50, regardless of CVSS — reflecting that exploitation probability and confirmed activity are stronger urgency signals than theoretical severity alone.
- Operationalizing this requires pulling all three scores automatically, applying the matrix consistently, committing to an SLA per tier, and re-scoring on a recurring basis — since EPSS and KEV both change daily in ways a one-time CVSS score never will.
| → Primary CTA: External Attack Surface Scan (Free) |
| Run your free External Attack Surface Scan at teisoftllc.com/free-vulnerability-scan/ and find out in minutes which findings on your external assets are genuinely high priority once CVSS, EPSS, and KEV are considered together. |
| → Secondary CTA: Continuous Penetration Testing |
| A combined CVSS/EPSS/KEV score tells you which findings deserve attention first. Teisoft’s Continuous Penetration Testing service goes further, confirming whether a top-priority finding can actually be chained into a real compromise in your specific environment. Contact Teisoft |
Related Resources on teisoftllc.com
Prioritization is the second of five stages in Teisoft’s CTEM cycle — see our guide to CTEM’s five stages for how it connects to discovery, validation, and remediation governance.
- CTEM Explained: The 5 Stages of Continuous Threat Exposure Management
- How to Read CVE Alerts: CVSS, Scope, and Priority
- Automated Exposure Validation: From Theoretical CVE to Confirmed Risk