Turn External Security Findings Into a Continuous Remediation Process
Teisoft Exposure Platform helps your team put CTEM into practice across your external attack surface—from identifying exposures to verifying fixes.
Discover internet-facing assets
Assess them for vulnerabilities
Prioritize risks
Coordinate remediation




Finding Vulnerabilities Isn't Enough
A security report can tell you what needs attention. Your team still needs to decide what matters most, coordinate the work, and check whether the fix addressed the exposure.
Bring those decisions into a connected workflow instead of piecing together asset lists, scan reports, and remediation updates.

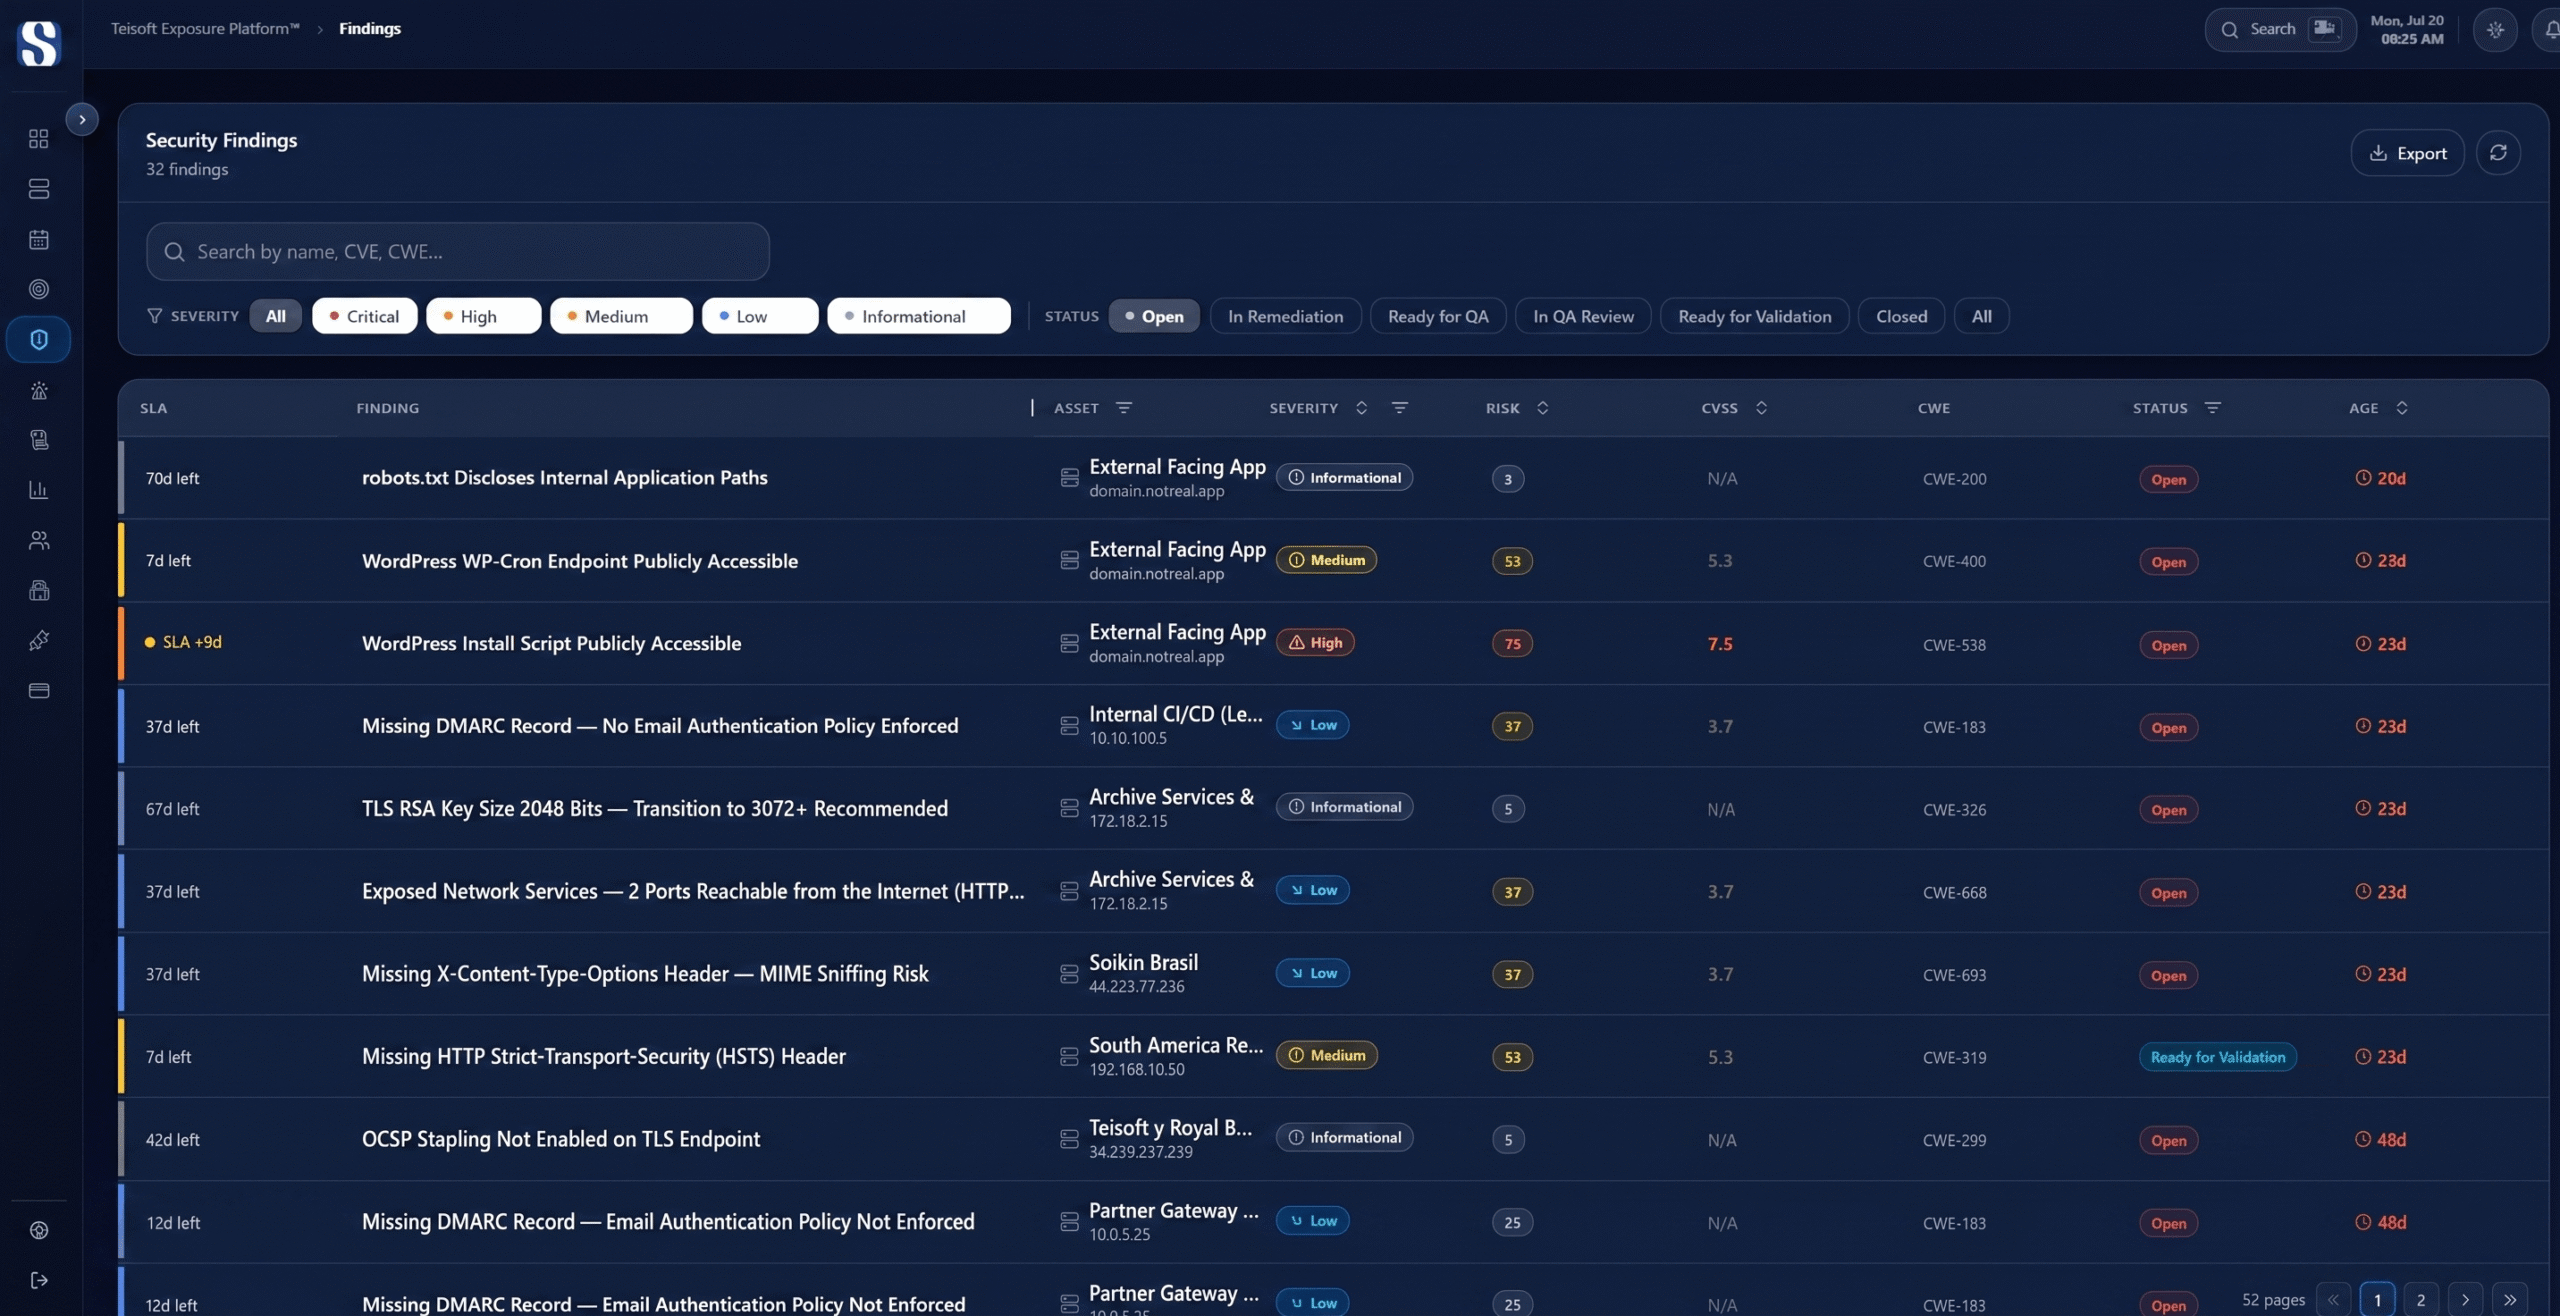

Discover Assets
Identify internet-facing assets and review the systems associated with your organization. Build the external inventory your exposure management process depends on.
Assess & Prioritize
Evaluate targets for vulnerabilities and misconfigurations. Use asset context, severity, and available evidence to decide what needs attention first.
Manage Remediation
Assign responsibility, track corrective work, and reassess affected targets after changes. Keep a record of what was found, what remains open, and what has been verified as resolved.
Full Platform Capabilities in Every Plan
Every plan includes the complete Teisoft Exposure Platform™ for managing your external attack surface. Choose the assessment capacity that fits your needss.
Full platform access with 5 Deep External Security Assessments included. For teams getting started with continuous external exposure management.
Start Free Trial- UNLIMITED External Asset Discovery & Inventory
- Continuous External Exposure Monitoring
- Prioritization, Remediation, Verification & Reporting Workflows
- 5 Deep External Security Assessments Included
- Additional Deep External Security Assessments available on demand.
Full platform access with 10 Deep External Security Assessments included. For growing teams managing a broader and more active external attack surface.
Start Free Trial →- UNLIMITED External Asset Discovery & Inventory
- Continuous External Exposure Monitoring
- Prioritization, Remediation, Verification & Reporting Workflows
- 10 Deep External Security Assessments Included
- Additional Deep External Security Assessments available on demand.
Full platform access with 25 Deep External Security Assessments included. For organizations managing higher assessment and remediation demand across a complex external attack surface.
Start Free Trial- UNLIMITED External Asset Discovery & Inventory
- Continuous External Exposure Monitoring
- Prioritization, Remediation, Verification & Reporting Workflows
- 25 Deep External Security Assessments Included
- Additional Deep External Security Assessments available on demand.
Core Platform Capabilities
Every plan includes the same core capabilities for continuously managing your external attack surface.
| Capability | Included in Every Plan |
|---|---|
|
01
Scoping
Define what should be monitored and establish ownership across your external attack surface.
|
|
| Attack Surface Scoping | Define and manage the external assets and infrastructure included within your organization's monitoring scope. |
| Monitoring Frequency Configuration | Configure how frequently your external attack surface is monitored based on your security and operational requirements. |
| Asset Ownership & Responsibility | Assign assets and security findings to the teams or individuals responsible for managing and remediating them. |
| Multi-Account Asset Management | Organize and transfer assets across accounts while maintaining centralized visibility and management. |
|
02
Discovery
Discover external assets, technologies, exposed services, and vulnerabilities.
|
|
| External Asset Discovery | Discover internet-facing infrastructure associated with your organization, including domains, subdomains, IP addresses, applications, and exposed services. |
| Subdomain Discovery | Automatically identify subdomains associated with monitored domains to uncover known and previously unknown internet-facing assets. |
| Network Service Discovery | Identify externally accessible network services running across discovered internet-facing infrastructure. |
| Port Scanning | Scan well-known ports to identify exposed network services and externally reachable infrastructure. |
| Shadow IT & Technology Detection | Identify technologies and unmanaged internet-facing resources that may exist outside your known asset inventory. |
| Web Application Security Scanning | Assess externally accessible web applications for vulnerabilities, security weaknesses, and potentially exposed components. |
| API Security Scanning | Assess externally accessible APIs and endpoints for vulnerabilities and security weaknesses. |
| Network Infrastructure Scanning | Analyze internet-facing network infrastructure for vulnerabilities, exposed services, and security configuration issues. |
| CMS Detection | Identify Content Management Systems and related technologies running across discovered web assets. |
| WAF Detection | Detect Web Application Firewall technologies protecting externally accessible applications and services. |
| TLS/SSL Security Audit | Analyze certificates, protocols, and TLS/SSL configurations to identify security weaknesses and configuration issues. |
| Vulnerability Assessment | Perform deeper security analysis across selected external assets to identify vulnerabilities and meaningful exposure. |
|
03
Prioritization
Reduce noise and focus your team on the exposures that require attention first.
|
|
| Risk-Based Prioritization | Correlate vulnerability, exposure, and threat context to help your team focus on the security issues that require attention first. |
| Finding Deduplication & Noise Reduction | Reduce duplicate findings and false positives to create a cleaner and more actionable vulnerability backlog. |
| Emerging Threat Alerts | Receive alerts when emerging threats may affect technologies or assets identified within your external attack surface. |
| Technology-Specific Threat Advisories | Receive security advisories relevant to technologies detected across your monitored external environment. |
|
04
Validation
Validate meaningful exposure and confirm that remediation was successful.
|
|
| Exploitability Validation | Actively validate identified vulnerabilities to determine whether they represent meaningful and potentially exploitable external exposure. |
| Remediation Verification | Rescan remediated assets to verify whether identified security issues have actually been resolved. |
|
05
Remediation & Governance
Coordinate remediation, maintain evidence, track progress, and demonstrate closure.
|
|
| Proof-of-Exploit & Technical Evidence | Capture technical evidence that helps security and remediation teams understand and validate identified exposures. |
| Vulnerability Evidence & Artifacts | Maintain supporting technical evidence and artifacts alongside vulnerability findings for review and remediation. |
| Remediation Evidence | Upload and maintain evidence documenting remediation work before verification and closure. |
| Remediation Guidance & Playbooks | Provide actionable technical guidance to help teams understand how identified vulnerabilities can be remediated. |
| Risk Treatment Workflows | Manage findings using flexible treatment workflows such as Fix, Accept, Transfer, or Mitigate while maintaining a record of the decision. |
| Vulnerability Lifecycle Management | Track vulnerabilities from discovery and assignment through remediation, validation, and closure. |
| Cross-Functional Collaboration | Coordinate vulnerability remediation activities across security, development, infrastructure, and QA teams. |
| Remediation SLA Tracking | Track remediation timelines and identify findings approaching or exceeding established remediation SLAs. |
| Security & Remediation Dashboards | Monitor external exposure, remediation progress, and operational security metrics through centralized dashboards. |
| Executive & Technical Reporting | Generate reporting for technical teams and stakeholders responsible for security oversight and governance. |
Frequently Asked Questions
How does the free trial work?
Onboarding is completely self-serve and takes less than five minutes. Upon registering your free account, you gain instant access to your security workspace and receive two full-scale, unthrottled external perimeter assessments. You can run these initial evaluations against any authorized target (domain, IP range, or cloud environment) to map your exposure profile immediately—no credit card required and no sales call scheduled.
Why does Teisoft offer unlimited assets and targets instead of per-asset pricing?
Legacy EASM tools penalize business growth by inflating your subscription cost every time your developers spin up a new cloud instance, staging subdomain, or API endpoint. Teisoft eliminates this “asset tax.” We discover and catalog your entire digital footprint (even if you have 10,000+ subdomains) for free. You only pay for the frequency of your active vulnerability assessments. You can easily rotate your scan capacity monthly across your assets based on their business criticality.
Can we monitor unlimited IPs and domains even on Starter plan?
Yes, absolutely. All Teisoft plans—including our Starter plan—include unlimited monitoring for IPs, domains, and subdomains.
We believe security teams should never have to restrict their scope or leave assets unmonitored to avoid licensing penalties. You can map and track 100% of your external attack surface at no extra cost; your subscription tier is based strictly on your monthly assessment quota (how often and how deeply you run security assessments), not on the size of your inventory.
How do monthly assessment quotas work?
Each month, you receive a dedicated pool of assessments to deploy across your unlimited target inventory. One assessment executes a deep-dive scan using ~30 specialized security tools against a specific domain, subdomain, or IP. You can schedule scans automatically or run them manually. Because different assets require different scanning frequencies, you can freely rotate your monthly assessment quota across different targets every billing cycle.
Do we need to install agents or configure complex cloud integrations to start mapping?
No. Teisoft is 100% agentless and externally non-intrusive. You can map your entire attack surface in under 5 minutes simply by entering your primary domains or IP ranges—no agents, no sensor deployment, and zero impact on your infrastructure.
Do you charge per seat, and can my development team log in to see findings?
No, we do not charge “per seat.” We believe security is a team sport . You can invite your entire technical organization—including developers, DevOps engineers, external compliance auditors, and sysadmins—to your Teisoft portal at no extra cost. You can assign finding owners, manage remediation workflows, and request automated re-scans the moment a patch is deployed, all within a single collaborative workspace .
What happens if we exceed our monthly scan pool or need an urgent, one-off assessment?
If you need more continuous coverage, you can dynamically upgrade your monthly scan pool inside your billing settings at any time. However, if you only have a temporary or urgent need—such as a single assessment for an upcoming compliance audit or a new software release—you can purchase individual scan credits on-demand with a single click, without committing to an ongoing plan upgrade. If you run out of monthly credits, the platform will notify you, but we will never automatically charge your card or block your continuous perimeter discovery workflows. You always maintain complete, transparent control over your security budget.